A cyberattack does not have to target your home directly to disrupt it. A compromised email account can expose your finances, a provider outage can block payments and communications, and an attack on critical infrastructure can interrupt power, fuel, water, or deliveries.
That is the practical meaning of cyber resilience at home. You do not need to predict who launched an attack or become a cybersecurity expert. You need layers: one layer that reduces the chance of compromise, another that limits the damage, and a final layer that keeps food, water, information, and communication available during an outage.
First, Identify Which Kind of Cyber Event You Face
“Cyber warfare” is often used as a catch-all term, but not every outage, scam, or ransomware incident is an act of war. For a household, the label matters less than the response. Most situations fall into one of three categories.
| Situation | Common warning signs | Your first move |
|---|---|---|
| Your account or device is compromised | Unexpected password resets, unfamiliar logins, unauthorized payments, new apps, locked files, or messages sent in your name | Disconnect the affected device and secure your email and financial accounts from a different, trusted device. |
| A provider is breached or offline | A bank, mobile carrier, cloud service, hospital, or retailer confirms an incident; one service is unavailable while others work | Use the provider’s official status page or known phone number. Do not follow links in surprise texts or emails. |
| A wider infrastructure disruption is underway | Multiple unrelated services fail, power or telecom networks are disrupted, official alerts are issued, or local supplies become delayed | Switch to your household outage plan, conserve battery power, and follow official local instructions. |

If You Think You Are Being Attacked Right Now
Move deliberately. Randomly deleting files, factory-resetting a device, or calling a phone number from a pop-up can destroy useful evidence or put you in contact with the attacker.
- Disconnect the affected device. Turn off Wi-Fi and Bluetooth or unplug its network cable. If files appear to be encrypting, disconnect external drives too. Do not reconnect your backup.
- Use a clean device and trusted connection. A different phone or computer is safer for recovery. Avoid signing into sensitive accounts on the suspected device.
- Secure your primary email first. Change its password, turn on multifactor authentication, review recovery addresses and forwarding rules, and sign out other sessions. Email often controls password resets for everything else.
- Protect money and mobile service. Call your bank or card issuer using the number on the card or its official website. Lock cards if available, report unauthorized activity, and contact your carrier if your phone suddenly loses service or you suspect a SIM swap.
- Change exposed passwords. Start with banking, password manager, cloud storage, mobile carrier, shopping, and social accounts. Never reuse the new password elsewhere.
- Preserve evidence. Photograph or capture suspicious messages, payment details, login alerts, ransom notes, dates, and case numbers. Keep a written incident timeline.
- Report and recover. Use IdentityTheft.gov for a personalized identity-theft recovery plan and the FBI’s Internet Crime Complaint Center to report internet-enabled crime.
How to Protect Your Home Before an Attack
The strongest household plan begins with a few repeatable habits. CISA’s consumer guidance emphasizes phishing awareness, strong passwords, multifactor authentication, and prompt software updates. Together, those basics block many common paths into an account or device.
1. Put every important account behind a unique login
Use a reputable password manager to generate and store a different password for every account. Where available, consider passkeys. Protect the password manager itself with a long, memorable master password and multifactor authentication.
Prioritize the accounts that can unlock everything else: email, Apple or Google accounts, your mobile carrier, banking, cloud storage, and the password manager. Save recovery codes offline in a secure place rather than only on the phone you may lose.
2. Turn on the strongest multifactor authentication available
Any multifactor authentication is better than a password alone. When a service offers choices, a passkey or physical security key generally provides stronger phishing resistance than a one-time text code. An authenticator app is also a useful option. Never approve an unexpected sign-in prompt; repeated prompts may be an attempt to wear you down.
3. Update—and replace—connected devices
Enable automatic updates for phones, computers, browsers, routers, smart-home hubs, cameras, and other internet-connected devices. Replace equipment that no longer receives security updates. Remove apps and accounts you no longer use.
4. Harden the home network
- Change the router’s default administrator password.
- Use WPA2 or WPA3 encryption with a strong Wi-Fi password.
- Install router firmware updates or enable automatic updates.
- Put guests and smart devices on a separate guest or IoT network.
- Disable remote administration and WPS if you do not need them.
- Review connected devices and remove anything unfamiliar.
5. Keep a backup that an attacker cannot reach
Back up irreplaceable photos, household records, and work files to more than one location. Keep at least one copy offline or otherwise separated from the devices it protects. A drive that remains plugged in can be encrypted by the same ransomware as the computer.
Backups are only useful if they restore correctly. A few times a year, recover several sample files and confirm that you can access them. Encrypt drives that contain sensitive information and store the recovery key safely.
6. Make scams harder to pull off
Criminals exploit urgent news, outages, and fear. Treat unexpected requests for passwords, verification codes, remote access, gift cards, cryptocurrency, or immediate payment as suspicious. Contact the person or company through a number or website you already know—not the link or phone number in the message.
Create a private family verification phrase for urgent requests. If a caller claims to be a relative in trouble, hang up and call that person or another family member directly. See our guide to protecting your family from AI-assisted scams for more verification habits.

Build a Household Continuity Plan
Cybersecurity protects data. Preparedness keeps daily life moving when a digital incident affects physical systems. Plan for the same practical consequences as a severe storm or regional power outage: limited communications, electronic payment problems, closed businesses, and delayed deliveries.
Keep a modest emergency cash reserve
Card terminals and ATMs may be unavailable even when the money in your account is safe. Store a household-appropriate amount of cash in a secure place, including small bills. Do not keep more at home than you can safely protect, and never withdraw savings based on an unverified rumor.
Store key information offline
Print emergency contacts, insurance phone numbers, prescription details, utility contacts, and the official web addresses for your bank and mobile carrier. Keep copies of essential records in a fire-resistant location or on an encrypted offline drive. Do not leave a plain-text list of passwords where it can be easily found.
Plan for power and communication
Keep charged power banks, compatible cables, flashlights, spare batteries, and a battery or hand-crank radio together. A properly sized power station can support phones and small medical or communications equipment; follow the manufacturer’s charging, ventilation, and storage directions. Never run a fuel-burning generator indoors, in a garage, or near doors and windows.
Choose two family meeting places—one near home and one outside the neighborhood. Designate an out-of-area contact who can relay messages. During network congestion, brief text messages may get through when calls do not.
Keep essential supplies on hand
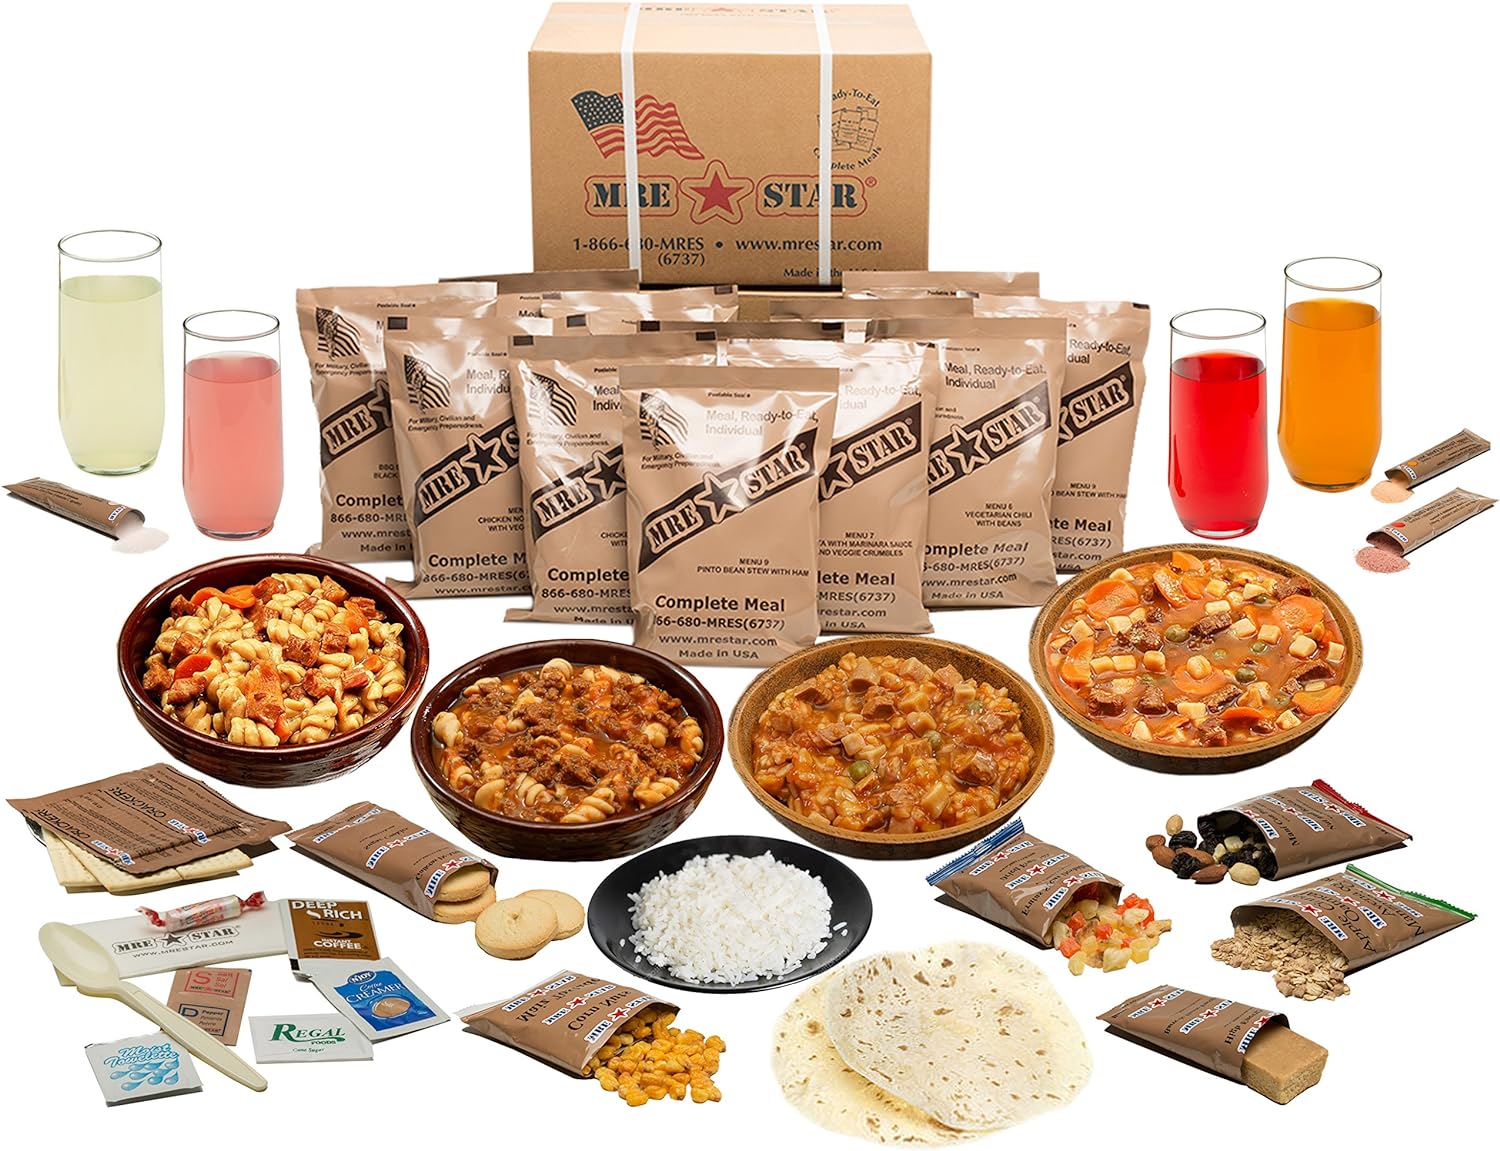
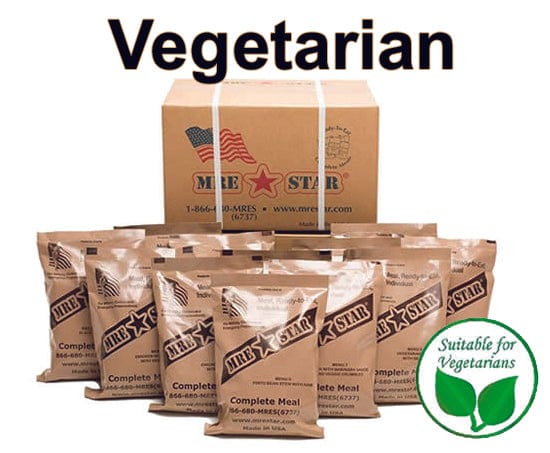
Maintain water, shelf-stable food, necessary medication, sanitation supplies, pet needs, and a manual can opener. Start with several days and build toward the level that fits your local hazards, household size, health needs, and storage space. Shelf-stable meals such as MRE Star M-018H ready-to-eat rations can provide a no-cook option when utilities or deliveries are disrupted.
What to Do During the First 24–72 Hours
First hour: verify and stabilize
- Check official emergency alerts, local government channels, utility notices, and provider status pages.
- If your device or account is affected, follow the isolation and account-security steps above.
- Switch phones to low-power mode and write down any important new information.
- Fill clean containers only if officials warn of a possible water interruption; follow any boil-water notice exactly.
First day: conserve and coordinate
- Use cash carefully and keep receipts when electronic systems are unavailable.
- Limit refrigerator and freezer opening during a power outage.
- Send one concise family status update rather than repeatedly calling.
- Delay nonessential travel if signals, fuel systems, or local services are disrupted.
- Record expenses, spoiled goods, outage times, and provider case numbers.
Days two and three: reassess with evidence
Check supplies, medication, batteries, and reliable information at set intervals. Avoid doom-scrolling, rumors, and panic buying. If a disruption is localized, arrange help through verified community contacts. If authorities issue evacuation or safety instructions, follow them promptly.
Financial and Identity Recovery After a Cyberattack
Once the immediate danger is controlled, review every affected account. Save confirmation emails and case numbers, dispute unauthorized transactions promptly, and watch for follow-up scams from people pretending to be investigators, bank employees, or recovery specialists.
Consider a credit freeze
If sensitive personal information was exposed—or if you simply want to reduce new-account fraud—contact Equifax, Experian, and TransUnion to freeze your credit. The Federal Trade Commission explains that a freeze is free, does not affect your credit score, and remains in place until you lift it. A fraud alert is different: it asks lenders to verify your identity but does not block access to your report.
Use the FTC’s credit freeze and fraud alert guide to reach the bureaus rather than relying on a sponsored search result or an unsolicited message.
Clean or rebuild affected devices
For a serious compromise, professional help may be appropriate. After preserving evidence, the safest recovery can involve erasing the device, reinstalling the operating system from a trusted source, updating it fully, and restoring only known-good data. Change passwords from a clean device before reconnecting the recovered computer.
Turn the incident into a stronger plan
Write down what failed: Was the email account the weak link? Were recovery codes inaccessible? Did every family member know whom to call? Did the backup restore? Fix those gaps while the experience is fresh, then schedule a short household review every six months.
Cyberattack Survival FAQ
Should I turn off my internet during a cyberattack?
If you believe a particular device is infected or actively being controlled, disconnect that device immediately. A news report about a broad attack is not, by itself, a reason to shut down every household connection. Follow instructions from your provider or public authorities.
How much cash should I keep at home?
There is no universal amount. Consider several days of essential purchases, your household budget, local risks, and how securely you can store it. Small denominations are more useful during payment outages. Keep most savings in protected financial accounts.
Is public Wi-Fi safe during an outage?
Do not assume a network is legitimate because its name looks familiar. Prefer your mobile connection or a network you trust, verify the hotspot name with staff, keep sharing turned off, and avoid sensitive transactions when possible. A VPN can protect traffic in transit but cannot make a fake website or infected device safe.
What should I do if I clicked a phishing link?
Stop interacting with the page. If you entered credentials, change that account’s password from a clean device, enable multifactor authentication, sign out other sessions, and change any reused passwords. If you downloaded or opened a file, disconnect the device and run the security steps recommended by its operating-system provider or a qualified technician.
Can I prepare without spending much money?
Yes. Start with free account protections, automatic updates, printed contacts, a family meeting plan, rotating extra food from your normal grocery list, and testing the backups you already have. Add equipment gradually based on the risks most likely to affect your household.
Final Takeaway
A cyberattack can be personal, commercial, or widespread. The best household defense covers all three possibilities: secure the accounts that control your identity and money, maintain recoverable copies of important data, and prepare for a temporary loss of power, communications, payments, or deliveries.
Begin with one hour this week: update your primary devices, turn on multifactor authentication for email and banking, print your emergency contacts, and verify one backup. Those four actions do more for real resilience than trying to predict the next headline.